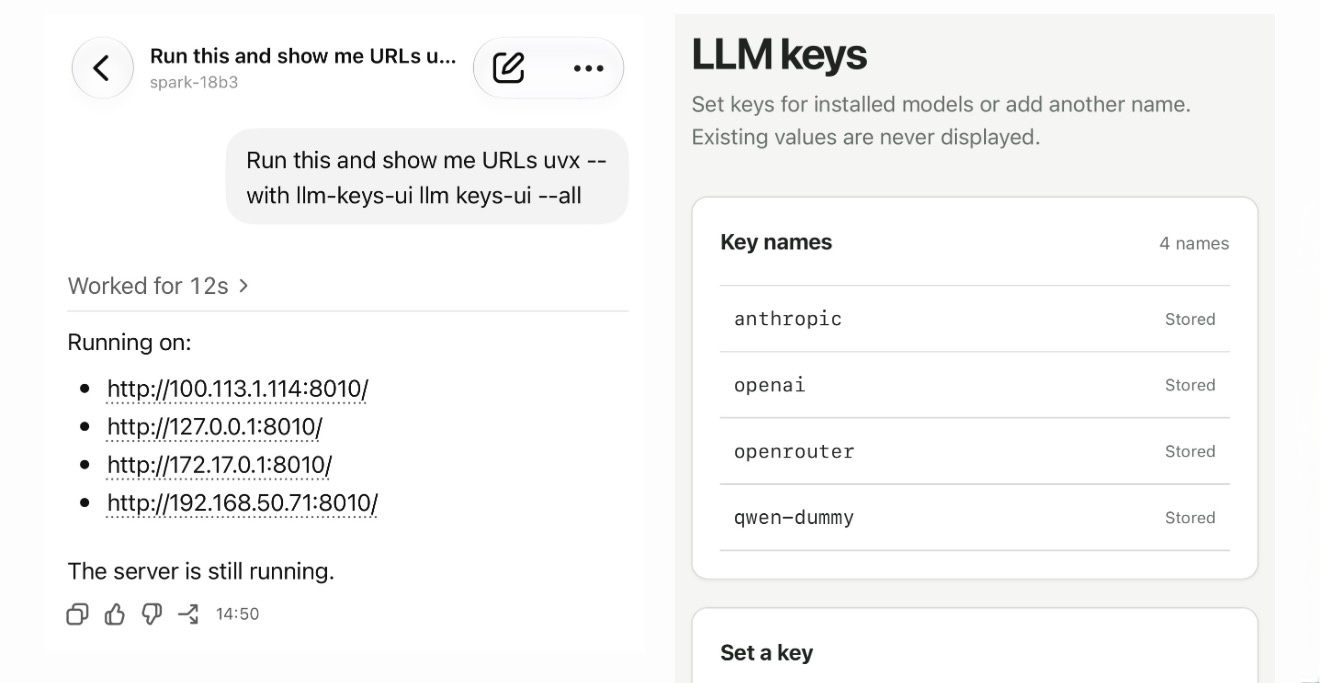
llm-keys-ui 0.1, published on 20 September 2026, lets developers load a key onto a remote machine through a local web page instead of typing it to the agent.
A proof-of-concept attack from Forever Security targets AI assistants in Chrome, Edge, Opera Neon, Perplexity Comet and Claude in Chrome, earning two CVEs.
Cybersecurity investors told The Register that firms are deploying AI agents faster than they can govern them, leaving a gap startups are racing to fill.
Researchers at Hacktron chained a help-forum bug with a login weakness to reach OpenAI employee accounts and an internal code repository, in authorised security research.
Senior AI executives told the consultancy their organisations are deploying autonomous systems faster than they are building the processes to supervise them.
Advisories published on 18 September 2026 describe token theft, an unauthenticated registry leak and server-side request forgery, all fixed in Obot v0.23.0.
A GitHub security advisory published on 18 September 2026 says Stacklok's ToolHive lets sandboxed MCP servers call the host, undermining its isolation model.
Hacktron researchers chained an image-parsing flaw in OpenAI's Discourse forum with an AI-written exploit, then opened a pull request in an internal OpenAI repository.
An unauthenticated remote code execution bug tracked as CVE-2026-58138 is being used against the workflow orchestration platform, SecurityWeek reported.
Dark Reading reported on 18 September 2026 that attackers used an AI-driven agent to get into a Spanish organisation's systems and change personal data.