
New plugin keeps API keys out of coding agent chat sessions
llm-keys-ui 0.1, published on 20 September 2026, lets developers load a key onto a remote machine through a local web page instead of typing it to the agent.
By The Agentic Times ·
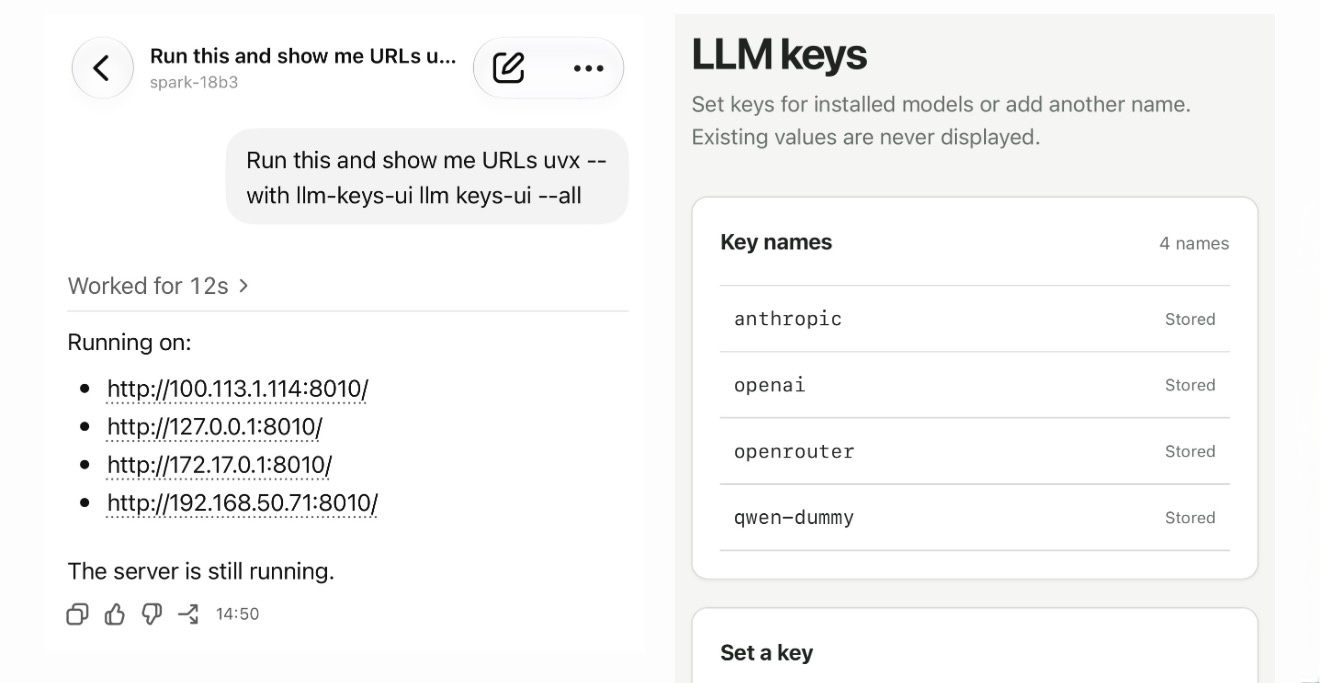
A new open-source plugin released on 20 September 2026 aims to stop developers from pasting API keys into conversations with coding agents. Called llm-keys-ui, the 0.1 release comes from Simon Willison, who described it on his own site as a fix for "a very specific problem" he ran into while running agents on remote machines.
The problem is a familiar one for anyone driving an agent from a chat interface. Willison said he has started using Codex Remote to run coding agents on various machines while controlling them from his phone. Sometimes those machines are used to work on LLM projects, and occasionally that work needs an API key configured. He said he does not like pasting API keys into agent sessions, and wanted a way to get keys onto a machine without typing them into the ChatGPT app directly.
The plugin works by adding a small web interface to the LLM command-line tool. According to the release note, the developer can tell the agent to run the command uvx --with llm-keys-ui llm keys-ui --all, then ask it to report back the URL for the interface. That URL can include local network or Tailscale device addresses, so the page can be reached from the phone that is driving the session. The key is then typed into that page rather than into the agent transcript.
Once the key is stored, the agent can retrieve it when needed. Willison said a later shell command such as llm keys get anthropic can be used as part of the agent's work when a key is required. The secret itself never appears in the chat history.
The design reflects a distinction that matters in agent security. A key pasted into a chat session becomes part of the conversation context, which may be stored, logged or sent on to a model provider. A key written into a local configuration store is available to commands running on the machine, but is not sitting in the transcript. The plugin does not remove the agent's ability to read or use the key; it changes where the key lives and who else sees it along the way.
This is a 0.1 release from an individual developer, not a hardened enterprise product, and the source does not describe any security review or threat model beyond the author's stated motivation. Readers running similar setups should note that the approach depends on the machine being reachable over a trusted network path, whether that is a local network or a Tailscale connection, and on trusting whatever the agent does with the key after it fetches it.
Sources
- simonwillison.nethttps://simonwillison.net/2026/Sep/20/llm-keys-ui