
Microsoft patches code execution flaw in Visual Studio Copilot
A path validation bypass let the Copilot coding agent write to its own settings files and run arbitrary commands, according to the researcher who reported it.
By The Agentic Times ·
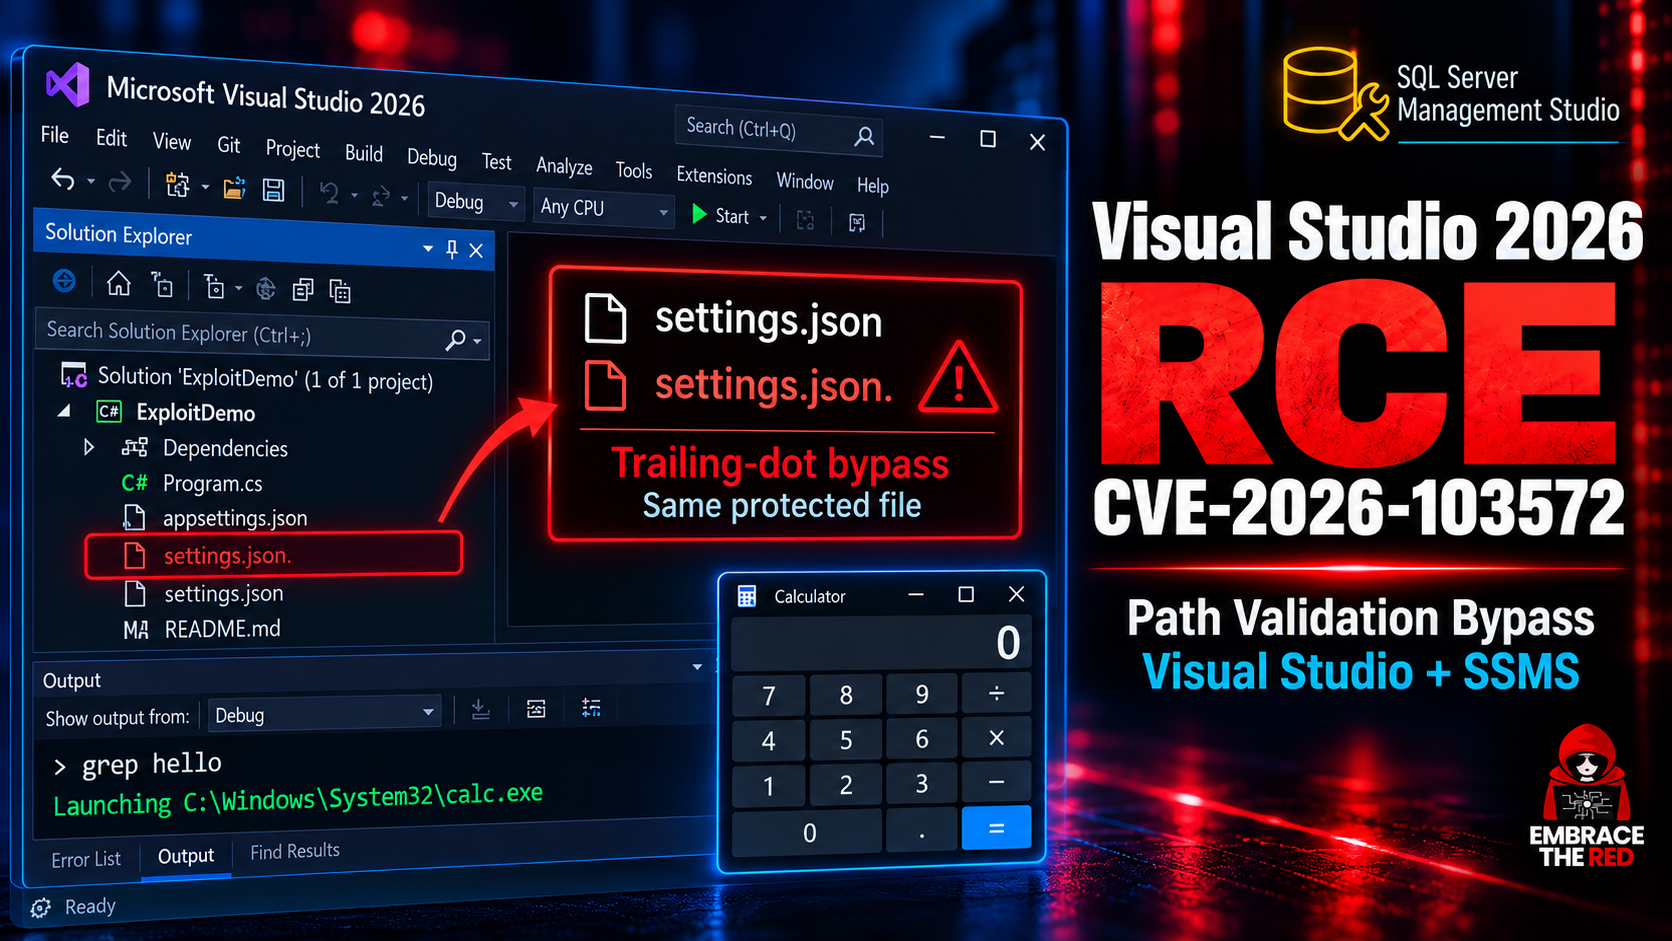
Microsoft shipped a patch on 13 October 2026 for a remote code execution vulnerability in Visual Studio Copilot and SQL Server Management Studio, tracked as CVE-2026-103572. The flaw was reported to Microsoft in August 2026 by the security researcher who disclosed it in a blog post published alongside the fix. Microsoft classified the issue as Important severity.
According to the researcher's write-up, the root cause was a path validation bypass. Copilot in Visual Studio or SQL Server Management Studio could get around a check on file paths and write to its own settings and configuration files. That, the post said, allowed Copilot to escape its containment restrictions and achieve arbitrary command execution.
The detail that made the bypass work was small. The researcher's post opens with the line "A . is all you need", a reference to the single character involved in defeating the path check. The write-up does not describe further exploitation steps beyond the write primitive and the resulting command execution.
The pattern is a familiar one for coding agents. Products such as Copilot run inside a developer's editor and are given the ability to read and write files in order to be useful. Vendors then wrap that ability in rules about which paths the agent may touch, and which actions need a human to approve them. Those rules are themselves usually stored in configuration files on disk. If an agent can write to the files that define its own limits, the limits stop being limits. In this case, according to the researcher, writing to the settings and configuration files was enough to break out of containment altogether.
The vulnerability sits in the category of tool misuse, where an agent's legitimate file-writing capability is turned against the controls meant to constrain it, rather than in a traditional memory safety or injection bug in the surrounding application.
Microsoft has issued a fix, and the issue is resolved. Users of Visual Studio Copilot and SQL Server Management Studio should apply the October update. The researcher did not report seeing the flaw exploited, and neither the blog post nor Microsoft's classification indicates in-the-wild abuse.
No further technical detail on the exploit chain, the affected version range, or the specific configuration keys involved was published in the source consulted for this article. The blog post was the only public account of the issue available at the time of writing.
Sources
- embracethered.comhttps://embracethered.com/blog/posts/2026/visual-studio-copilot-remote-code-execution