
Symlink flaw let Jan's coding agent write files outside workspace
CVE-2026-122235 affects Jan 0.8.5 up to 0.8.8 and could be triggered by prompt injection hidden in a malicious repository, according to the NVD entry.
By The Agentic Times ·
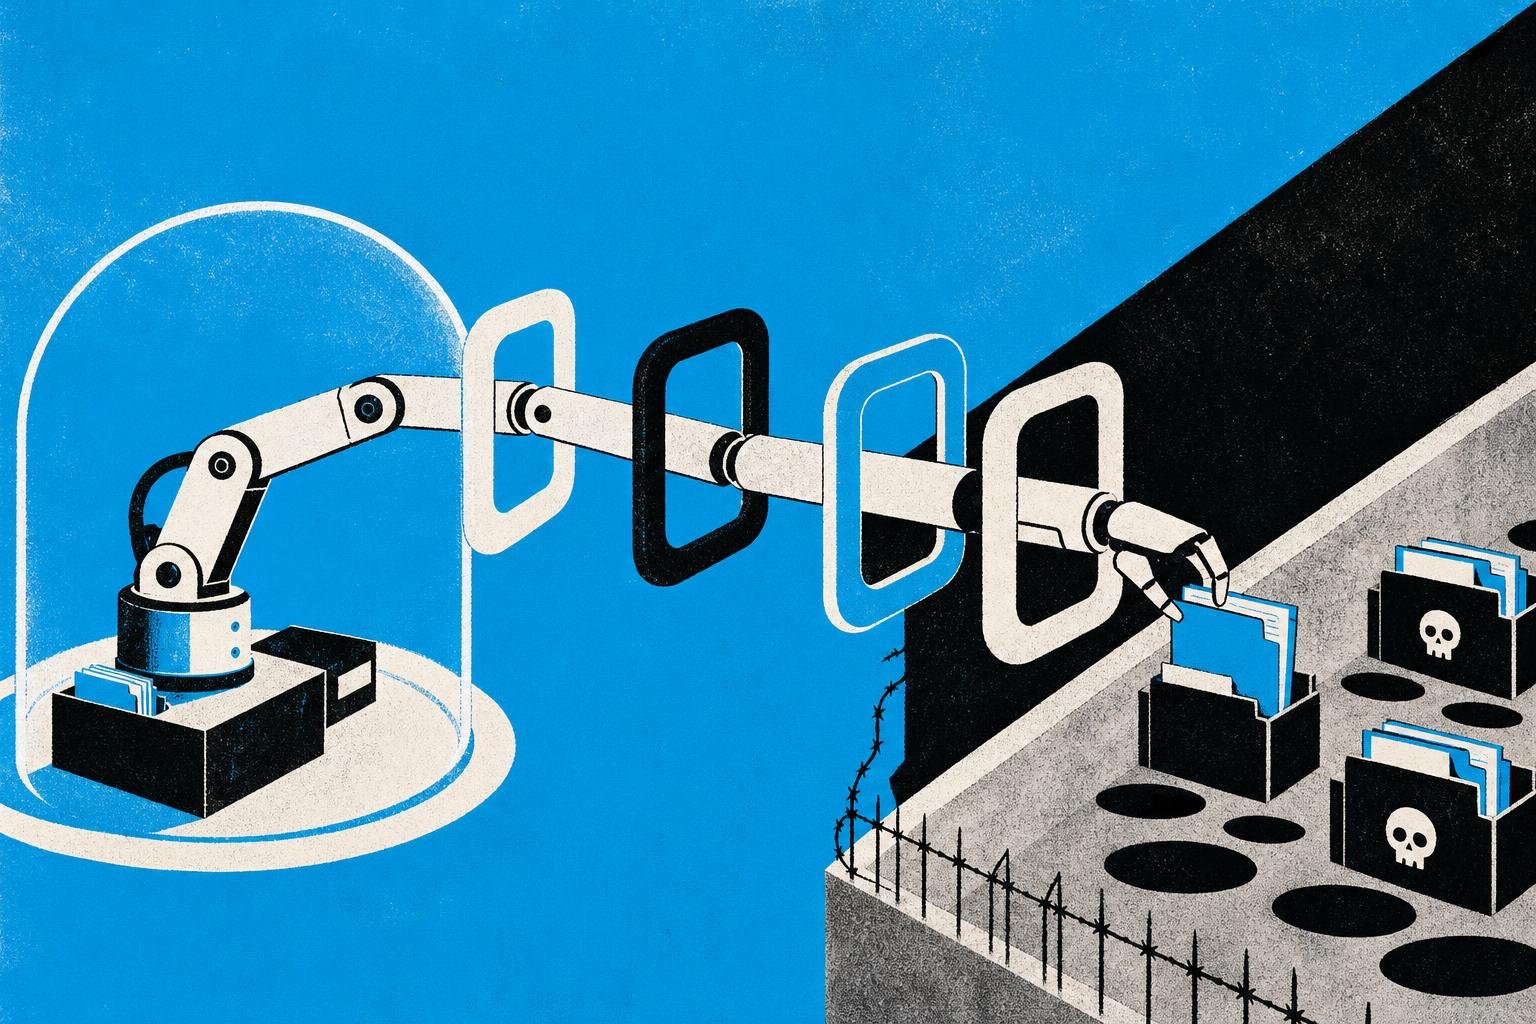
A vulnerability in the AI assistant Jan allowed attackers to write files anywhere on a user's machine, bypassing the sandbox that is supposed to confine the agent's file operations to a single working folder. The flaw was published in the US National Vulnerability Database on 4 November 2026 as CVE-2026-122235. It affects Jan from version 0.8.5 up to, but not including, version 0.8.8.
According to the NVD entry, the problem sits in the agent-tools component, specifically a file called gate.rs. That code acts as a workspace guard, the check that is meant to stop the agent's tools from touching anything outside the directory the user has opened. The guard could be bypassed using dangling symlinks, which are symbolic links pointing at a file that does not yet exist. Because the target was missing, the guard apparently did not resolve it to a path outside the workspace, so the write went ahead and followed the link.
The attack path described in the advisory starts with a malicious repository. An attacker who supplies a repository for the agent to work on can plant instructions inside it, a technique known as prompt injection, in which text in data the model reads is treated as a command. The NVD entry says this can be used to make Jan's write or edit tools follow the symlinks. The example given is the creation of a file at ~/.ssh/authorized_keys on the host machine. That file controls which keys may log in over SSH, so writing to it is one of the more direct ways to turn a file write into persistent access to a computer.
The pattern is a familiar one for coding agents. The agent is given tools that write files, a guard is added to keep those writes inside a project folder, and the guard is then defeated by an edge case in how paths are resolved. What makes it worse in an agentic setting is that the attacker does not need to run code on the victim's machine directly. Supplying a repository and getting the agent to read it is enough, because the agent itself holds the file-writing permissions.
Jan's maintainers have shipped a fix. The NVD entry references a commit and a pull request in the janhq/jan repository on GitHub, along with the release notes for version 0.8.8 and a security advisory published through GitHub's advisory database as GHSA-7j4g-mj5j-p842. A corresponding advisory has also been published by VulnCheck. Users on affected versions should move to 0.8.8 or later.
The listed sources do not say whether the flaw was exploited against real users, who reported it, or what severity score has been assigned. They also do not state how the issue was discovered. The record available at the time of writing describes the vulnerability as confirmed and fixed in the 0.8.8 release.
For anyone running coding agents against untrusted code, the practical lesson in this advisory is narrow but useful. A workspace boundary is only as strong as the path resolution behind it, and symbolic links that point nowhere are an easy case to miss. Treating any repository the agent reads as potentially hostile input, rather than as inert data, is the assumption that this bug rewards.
Sources
- nvd.nist.govhttps://nvd.nist.gov/vuln/detail/CVE-2026-122235