
BragJack attack turns browser AI assistants against users
Dark Reading reports a new technique that hijacks the AI assistants built into browsers to reach sensitive data and carry out actions on a user's behalf.
By The Agentic Times ·
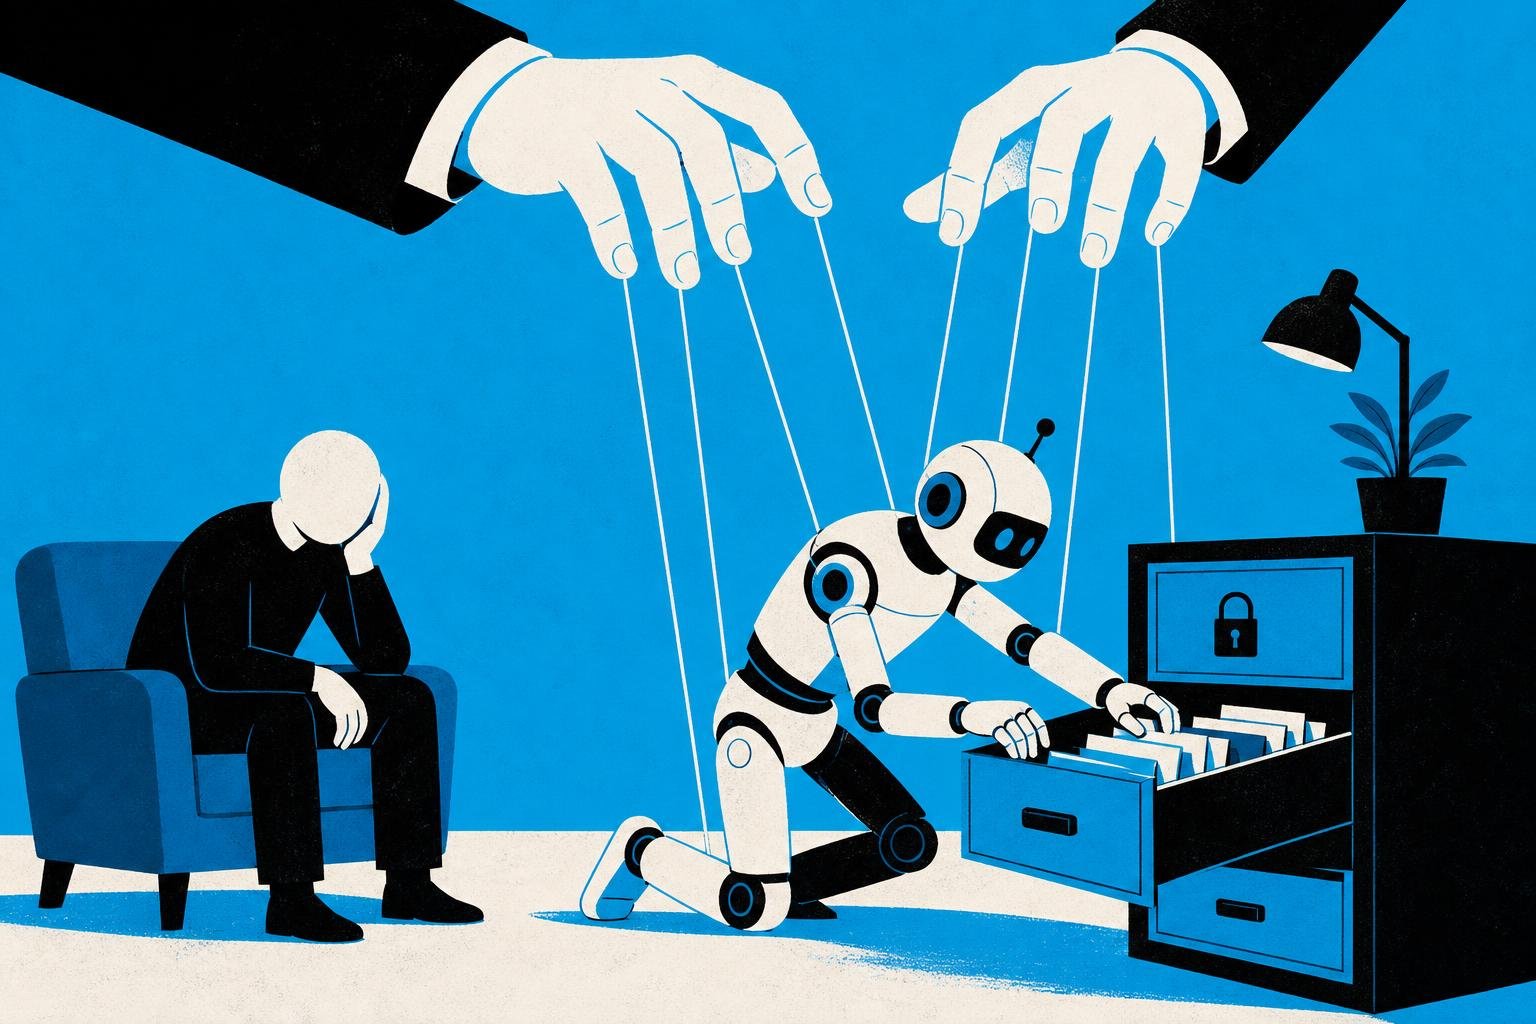
A newly identified attack technique called BragJack can hijack the AI assistants built directly into web browsers, using them to access sensitive information, execute malicious actions and exfiltrate data, according to a report published by Dark Reading on 16 September 2026.
The report describes BragJack as a new type of attack that turns a browser's agentic AI against the browser itself. Agentic AI, in this context, means an assistant that does not simply answer questions but can take actions inside the browser on the user's behalf, such as reading pages, filling forms or moving data between sites. That is precisely the capability the attack abuses: according to Dark Reading, the hijacked assistant becomes the route to the user's data rather than a target that must be broken into.
Dark Reading says the technique affects the AI assistants built into various browsers, rather than a single named product. The report as published does not identify the affected vendors, the researchers behind the finding, or the specific mechanism by which the assistant is hijacked. It also does not state whether the attack has been seen used against real users, or whether patches or mitigations are available.
Three consequences are named in the report. The first is access to sensitive information, meaning data the assistant can reach because the user is already logged in to it. The second is the execution of malicious actions, meaning the assistant performing steps an attacker wants rather than steps the user asked for. The third is exfiltration, the security term for data being moved out of a system to somewhere an attacker controls.
Beyond those points, the details are thin at the time of writing. There is no published severity score, no vulnerability identifier and no vendor advisory referenced in the source. The Agentic Times has not independently verified the technique, and the incident is recorded here as reported rather than confirmed by an affected vendor.
For organisations that have rolled out browsers with built-in AI assistants, the practical question raised by the report is a narrow one: what can the assistant see and do inside a logged-in browser session, and who else can influence it. Until fuller technical detail is published, that scope is the only part of the picture defenders can measure for themselves. We will update this story if vendors respond or if the underlying research is released in full.
Sources
- darkreading.comhttps://darkreading.com/endpoint-security/bragjack-browser-agentic-ai